Defensible Academy × Clovera.io · In-house program
The AI-Working OrganizationFrom Pilot to Daily Practice
Your people actually use AI. Your organisation can stand behind it.
After two days, every participant leaves having rebuilt three tasks from their own job with AI, with the time saved measured. The organisation leaves with four board-ready deliverables: an AI inventory and risk classification, an employee AI use policy, a vendor and evidence file, and a 90-day deployment plan.
Usage is at 90 percent. Training is at 33. The gap between them is what we sell.
90%
of organisations have employees using AI; only 33% provide formal training
ISACA 2026 AI Pulse Poll, 3,400+ professionals
86% → 25%
of CEOs believe their workforce is AI-ready; 25% of employees use it regularly
IBM 2026 CEO Study, 2,000+ CEOs
56%
are not sure how quickly they could shut their AI systems down
ISACA 2026
$186
monthly cost per employee of fixing polished but empty AI output
HBR / BetterUp Labs, September 2025
Your employees paste sensitive data into these tools roughly every three days, and half of them hide it from their manager. Turkey's data authority named this in its 5 March 2026 announcement: shadow AI. What it expects is a written policy, human oversight and employee training.
The difference
In the world's most expensive executive AI programs, keyboard time is 5 to 15 percent. Here it is 40.
We went through Wharton, Kellogg, Stanford and INSEAD, the Big Four academies and the free vendor curricula one by one. Nobody puts participants in front of their own organisation's data, at their own desk, building their own tool. Nobody makes local regulation, the vendor contract and the evidence file a working object. This program was written into exactly that gap.
Elite school program
Consulting academy
Vendor content
This program
Hands-on share
5 to 25%
mostly asynchronous
100% but generic
40%, visible in the day plan
Local regulation
none
generic
none
KVKK, BDDK, DIFC, CBUAE, AI Act
Vendor contracts
none
rare
none
a working object
Evidence file
none
measurement, no evidence
none
the centre of the product
Written for
C-suite
mixed
end users
mixed teams, middle management included
After the classroom
none
billed separately
none
day 30 and day 90 included
Framework
Four Layers
The spine of the program is four questions. The first three exist in some form in every good program. The fourth, evidence, is produced by no certification, no elite program and no free vendor content. We put it at the centre.
01
DATA
What goes into AI, and what never does?
Data classification and a decision tree. Enterprise versus personal accounts. Anonymisation versus pseudonymisation, indirect identifiability, cross-border transfer.
02
USE
How is the work actually rebuilt?
Every laptop open. Workspace setup, document work, a verification protocol, automation and the limits of agents, on the three tasks each participant brought.
03
CONTROL
Who approves, who monitors, who stops it?
AI inventory and risk classification, three lines of defence, the corporate counterpart of NIST AI RMF and ISO 42001, LLM-specific risks, reporting to the audit committee.
04
EVIDENCE
What do you show the auditor, the board, the regulator?
A regulatory decision tree, a vendor contract workshop, the employee use policy, incident handling, and a record of who was trained when, in which role, with which content.
Flow
It starts before the training and ends after it.
The two classroom days are the middle of the program. Without a baseline beforehand, no return can be proven; without follow-up afterwards, what was learned evaporates within a quarter.
Phase 0
Pre-diagnosis · 2 to 3 weeks before
Anonymous shadow AI survey: which tools, for what, on which account, with which data
Clovera AI Governance Scorecard for every participant
Baseline: the three real tasks each participant will bring, and how long they take today
Document collection: any existing policy, one vendor contract, one internal procedure
The output is the opening slide of Day 1: "In this company, 14 people use 6 different AI tools, 9 of them enter customer data, and none of them told their manager."
Day 1
Data and Use
Everyone works on their own job. The day ends with a measured number.
09.00
A common language and the company's real AI map
Survey results. The shape of risk in 2026: LLMs, agents, shadow AI. Named cases: Air Canada, Samsung, Deloitte Australia. What an agent actually is, and is not.
OutputThe organisation's AI use map, first draft
10.30
DATA layer: what goes in, what never does
The decision tree. The operational meaning of the KVKK announcement of 5 March 2026. Live: working through a document with an anonymisation tool.
OutputThe AI data-entry rule, one page, written together on screen
13.15
USE layer: rebuilding the work
The longest block of the day, four hours. Workspace setup, document work, the verification protocol, the workslop lesson, automation and agents. Parallel department labs: legal and compliance, finance and internal audit, HR, sales and marketing.
OutputThree tasks rebuilt and timed, a personal prompt library, a department playbook
17.15
Measurement
Time saved across the three tasks is added up, written on the board, multiplied by headcount and annualised. The client works out what the program is worth with that number, not with ours.
OutputMeasured annual time saving
Day 2
Control and Evidence
Which of yesterday's work belongs in the inventory, and which of it is high-risk.
09.00
CONTROL layer: governance, risk, audit
AI inventory and classification. Governance architecture: roles, committee, policy set. How three lines of defence work for AI. Prompt injection, data leakage, model changes, black-box risk. Reporting to the audit committee.
OutputAI inventory and risk classification, RACI, top five risks and their controls
13.15
EVIDENCE layer: regulation, contracts, policy
A regulatory decision tree: AI Act role and class, Article 4 after the Digital Omnibus, KVKK, DIFC Reg 10, CBUAE. The client's own vendor contract on the table; twelve clauses for an AI addendum. The employee use policy is written in the room.
OutputAI Act role and class card, vendor AI addendum checklist, draft employee AI use policy, incident response flow
16.15
Deployment: 90 days
The champion network: one champion per 15 to 20 employees, three to four hours a week at most. Use-case inventory and scoring. The measurement dashboard and month-six thresholds. Teams present a one-pager to the board; we critique it.
Two 60-minute online check-ins, a baseline comparison and a short written report. Two elite programs do this; consultancies bill it separately.
Deliverables
Four board-ready deliverables
01
AI inventory and risk classification
Every AI system running in the organisation, its role, risk tier and owner in one table. The OECD framework and AI Act tiers side by side.
02
Employee AI use policy
What is allowed, what is not, who approves, what happens on breach. Written in the room from that organisation's real usage; not a template.
03
Vendor and evidence file
The AI addendum checklist, the model provider's terms as actually read, and a record of who was trained when, with which content.
04
90-day deployment plan
Champion list, use-case inventory, measurement dashboard and the single page that goes to the board.
Twelve documents every participant keeps
01 AI use map
02 Data-entry rule
03 Personal prompt library
04 Three rebuilt tasks with measured time
05 Verification checklist
06 Department playbook
07 AI inventory and risk classification
08 RACI and control checklist
09 AI Act role and class card
10 Vendor AI addendum checklist
11 Draft employee AI use policy
12 90-day plan and board one-pager
Instructors
One rebuilds the work. The other makes sure you can stand behind it.
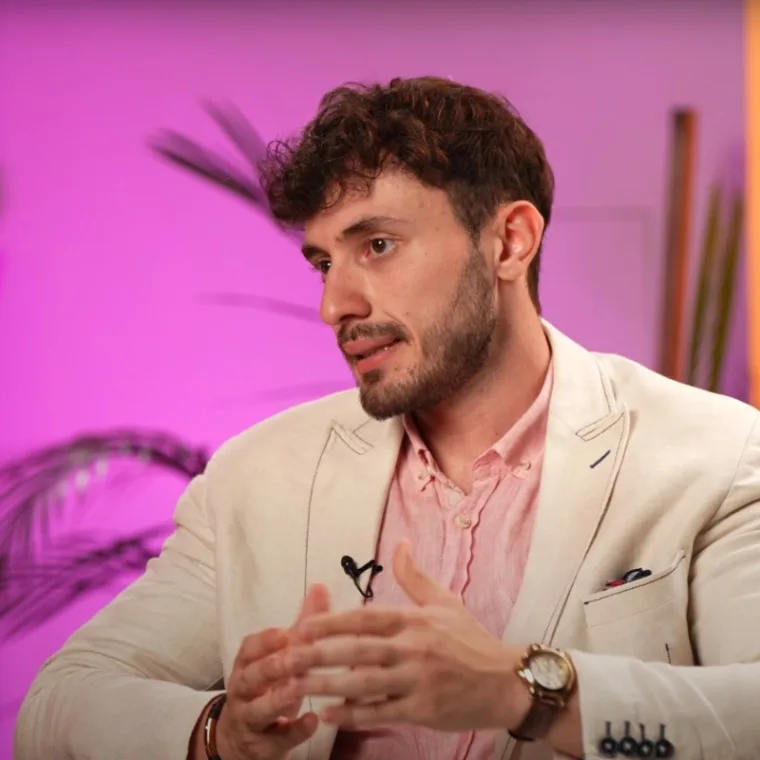
Alp Mete Şirin
Founder, Defensible Consultancy · Istanbul and Dubai
Advises AI, Web3 and fintech companies on market entry, product structuring and cross-border regulatory strategy. Has trained hundreds of lawyers in practical legal AI. Leads the Data, Use and Evidence layers.
KVKK
EU AI Act
DIFC
Contracts
Applied AI
Gökhan Polat
Founder, Clovera.io · CISA, CISM, CISSP
Over twenty years across public and private sectors; strategic roles at EY Turkey, SabancıDx and Paribu, founder of Noode, Turkey's first NaaS platform. Member of the ISACA Emerging Technologies Advisory Group and Cloud Security Alliance Turkey. Leads the Control layer and the audit side.
AI Governance
Risk
Internal Audit
ISO 42001
NIST AI RMF
100+
corporate training sessions
Gökhan Polat
28
completed projects
Clovera.io
13+
startups that closed a funding round
Defensible
20+
years of enterprise experience
Gökhan Polat
Organisations we have trained and worked with
In the press
Regulatory anchor
Four regulators point at the same gap: evidence.
The program is not a rival to certification; it is the implementation layer. AIGP teaches you the framework. We leave you the inventory of your forty AI systems, your role-based training matrix and your evidence file.
Türkiye
KVKK · announcement of 5 March 2026
Names shadow AI as a risk and expects a written use policy, access rules, human oversight of outputs, and awareness and training activities for employees.
European Union
AI Act Article 4 · after the Digital Omnibus
Rewritten on 24 July 2026: from an obligation of result to an obligation of means. Most training on the market still sells the old text. The Commission's FAQ expects an internal training record; the curriculum is mapped to the AILit framework.
Dubai · DIFC
Data Protection Regulation 10
Deployer and Operator roles, human oversight, a use-case register and evidence of compliance. An Autonomous Systems Officer for high-risk processing.
UAE · Central Bank
CBUAE · guidance of 11 February 2026
A documented governance framework, a model inventory, bias stress testing and proportionate human oversight. Responsibility for AI outputs stays with the institution even when outsourced.
This program supports the fulfilment of obligations under Article 4 and the KVKK announcement; it does not constitute or guarantee compliance. We tell nobody that it "proves your compliance" or that "you will not be fined". What we leave behind is a record: hours, content version, role mapping and date, per participant.
Format
An in-house cohort. Not open enrolment.
Who it is for
A mixed team: legal and compliance, finance and internal audit, HR, sales and marketing, IT. Not only executives; adoption is measured in middle management.
Size and place
12 to 20 participants, minimum 8 per organisation. On site or online. Istanbul, Dubai, or your own office.
Language
English or Turkish. Materials in both; the KVKK and DIFC blocks are weighted to the organisation's jurisdiction.
Certificate and CPE
A joint Defensible Academy × Clovera.io certificate of attendance: hours, learning outcomes, role mapping, content version and date. Directly usable for IAPP and ISACA CPE self-reporting; meets ISACA's AI-focused CPE requirement.
Path
The two-day program is the middle step.
0
AI Status Diagnosis
2 weeks. Shadow AI survey, scorecard, draft inventory, regulatory exposure map. Can be bought alone; credited if you continue to the program.
1
Board Briefing
3 hours. Twenty minutes of live work on the company's own document in front of the board, then five questions. The last one: how quickly could we shut our AI systems down?
2
Main Program
2 days, in-house, 12 to 20 people. This page.
3
90-Day Sprint
Two tracks. Deployment: department workflows, champion network, weekly office hours. Governance: inventory, policy set, ISO 42001 gap analysis, contract addenda, board presentation.
4
Annual Retainer
Regulatory updates, an onboarding module for new staff, quarterly measurement, an annual refresh. The Article 4 and KVKK expectations are continuous.
Frequently asked
Our team is not technical. Can they keep up?
The program was written precisely for non-technical teams. The first module builds a common language; in the third, everyone works on a task from their own job. Nobody writes code. Tools are set up, documents are processed, outputs are verified.
We already have Copilot or ChatGPT Enterprise licences. Why train separately?
A licence is not usage. IBM finds 86 percent of CEOs believe their workforce is ready while 25 percent of employees use AI regularly. Generic training sustains adoption at 23 percent; role-based training at 67. The program turns the licence into work, and measures it.
How will we prove the return?
Before the training, each participant's three tasks are timed as they are today. By the end of day one the same tasks are rebuilt and re-timed; they are measured again on day 30 and day 90. The team in the room does the arithmetic, not us.
Is this a compliance certificate?
No, and be wary of anyone who says theirs is. The certificate shows who was trained, when, in which role, with which content version. That is the internal record the KVKK announcement and AI Act Article 4 expect; it is not compliance itself.
Do we hand our data to you?
No. Participants work with their own documents in their own enterprise accounts. That is exactly what the second module is about: what goes into AI and what never does. The pre-diagnosis survey is anonymous.
Can it be delivered online?
Yes. The department labs in module three run in parallel rooms. In-person delivery makes the measurement moment stronger; we do both.
Why two instructors?
Use and control are different disciplines, and when they come from one person, one of them is weak. Alp rebuilds the work and turns regulation into a working object; Gökhan brings twenty years of audit and governance practice so the organisation can stand behind it.
Start
Let's make what your team already uses governable.
Tell us your organisation, the size of your team and the problem that brought you here. In a 15-minute call we agree which step to start from; the pre-diagnosis survey is free.